She's from Netscaler, I can tell by the way he's payloading
Threat intelligence and hunting notes on Netscaler activity.
Let's talk about Netscaler
A good chunk of this is sourced from other people, I'm attempting to collate it together into a useful product. No promises. If I missed you as sourcing, I really apologize.
By DelightfullyStupid
If you haven't been living under a rock in the intelligence or hunting world, you've probably seen this pop up over the week.
Allegedly the Dutch figured it out first and starting flirting the info out to the world, which forced Citrix to respond and patch. Unfortunately, it looks like the CVE has been actively exploited since...August? Early September? Kiteworks, I thought your strategy was way cooler.
The good news is there's a patch out, so yay for all you engineers who got paged this last weekend.
First things first - Watchtowr has a few great posts on the Netscaler CVE 1 and 2.
Unfortunately here we are a week later and there's a new CVE in town. Fresh off the presses, CVE-2026-88779.
Now I know what you're thinking, dad why do you hate me. Good question son, its not me, its 3 zero days in 6 days.
This kicked off with our best friend Kevin Beaumont.
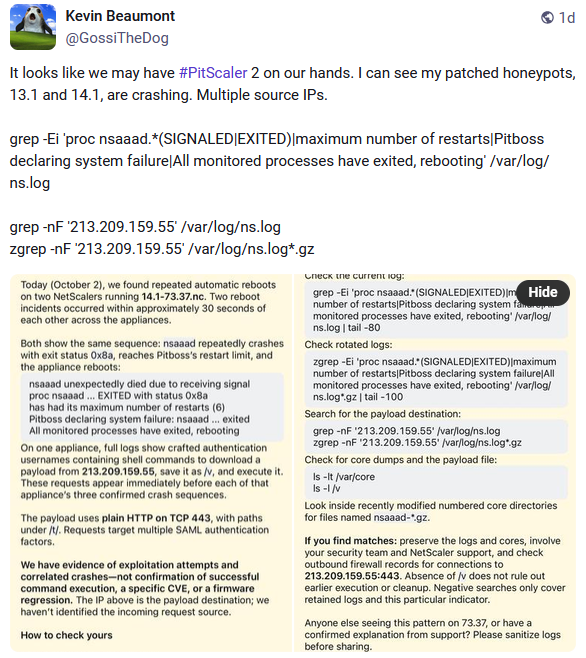
Based on observations seen in the wild, the IP in the photo 213.209.159[.]55 is not just a payload dropper, it also has been seen attempting some of the older CVEs. Reporting also has the actor utilizing f.pylrk[.]cc/somepath
This does not mean this IP address and domain are the only things worth looking into. Ultimately, it allegedly just drops Sliver 0188b0eba4b01c4fb838df9d1d76c76d7f1dc22897e25161975b606c134c1027
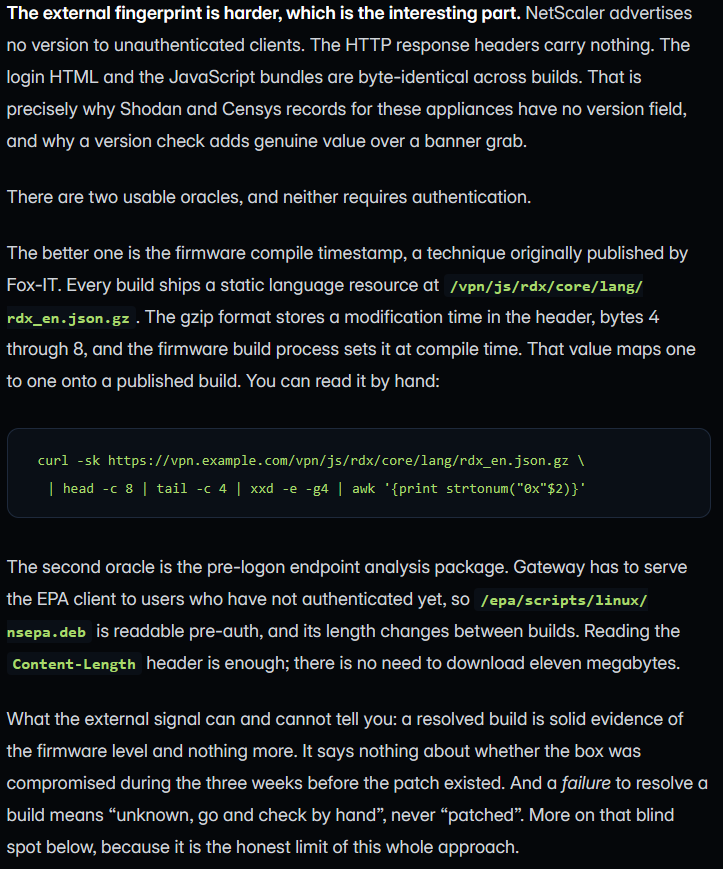
IF you're fortunate and your logs get forwarded to your SIEM, there's a few things to look for. The first two CVEs which are well documented, but checking ns.logs would be prudent. An interesting thing I stumbled onto is you can easily check if you're being fingerprinted:
From Reddit sourcing, it appears the vulnerability is primarily a DoS. Kevin saw a successful payload, but reporting around that is iffy. It seems to mostly be forcing Netscaler restarts.
Couresty of delishouscake:
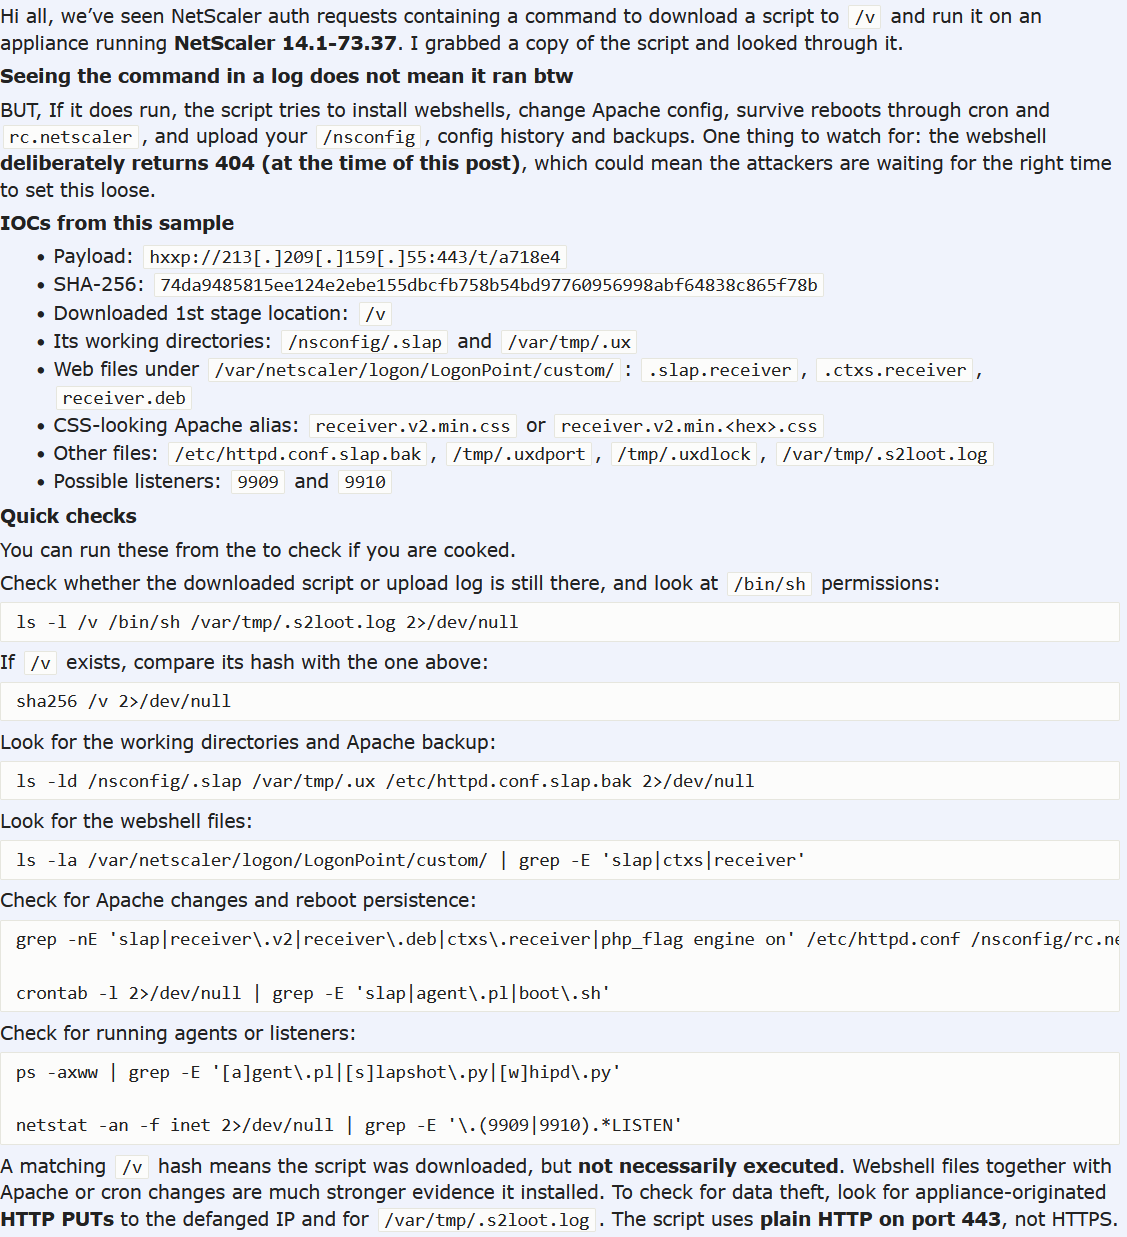
Based on my analysis and perusing the depths of reddit, twitter, and bluesky, this is likely an alt. step to the first two CVEs. There's some limited information floating around that they require a log rotation to execute. By forcing crashes/restarts, they're forcing the exeuction. With their operation being blasted, it's possible they're finalizing their targeting list and applying this third CVE to get footprints into priority targets.
If we think about this campaign which I'm sure vicitim analysis will come out later, the threat actor is burning multiple n-days, utilizing a substantial amount of resources, and appears to have good-decent operation security. More than likely, it's an advanced nations B team, contractors, or maybe a fairly advanced cybercrime group.
Ultiumately, my verdict with low-moderate confidence is it's:
For my Threat Hunting Kings:
If your netscalers are still up, look for webshell activity. Pitscaler is a sick resource a lot of details on all the CVEs, detection strategies, and IoCs for your SOC.
If your netscalers are down, I hope your logging is good.
If your netscalers are down and your logging sucks, look for lateral movement.
If you're netscalers are down, your logging sucks, and you find no lateral movement, hope you're good...otherwise we'll see you in some 10ks!
See ya'll next friday for the next Netscaler CVE drop.